What security, customer service and AI reveal about our struggle to understand each other—and act before something goes wrong.
Cyberattacks and data leaks have become familiar headlines. Behind those headlines are people: customers who cannot use a service, employees trying to help without working systems, and families wondering where their personal information has ended up.
What frustrates me is the gap between noticing a problem and getting something done about it. A warning can be clear to the person giving it and still mean very little to the person who has to make a decision.
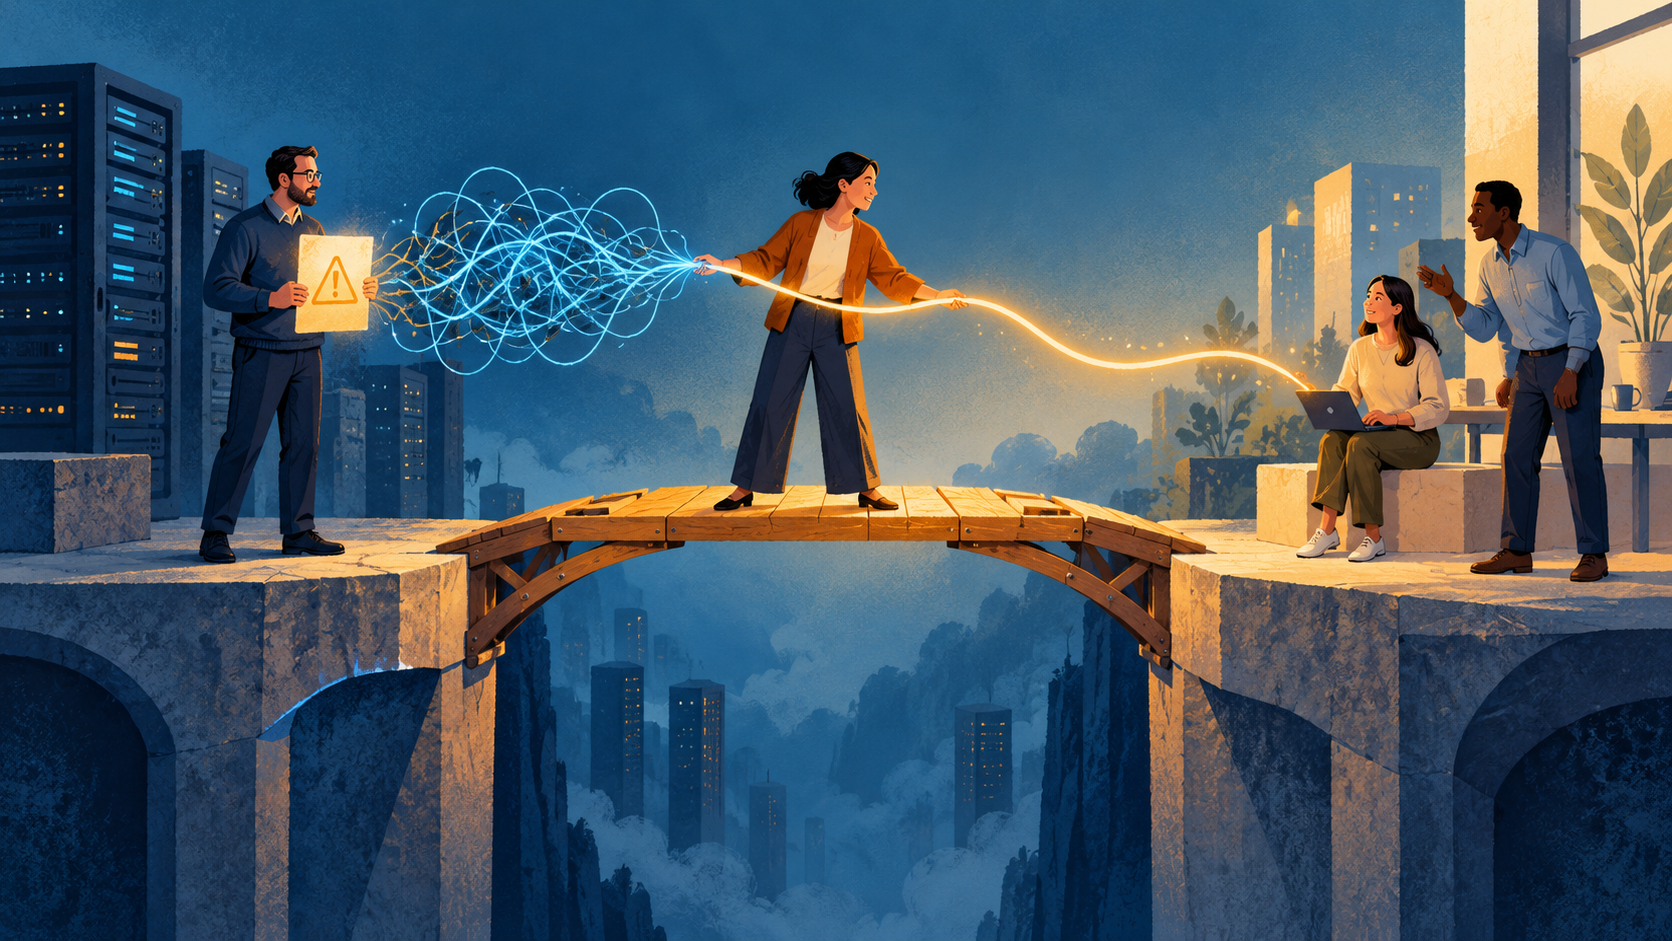
I recognise that gap in cybersecurity. I see it in discussions about AI, creative work and data centres too. We share a world, but we often explain it from separate islands.
Why security and service clash
Imagine a company director, a security specialist and a customer service worker discussing the same system.
The director needs to keep the business running and pay its bills. The security specialist wants to stop accounts being stolen and information being exposed. The service worker wants to help a customer quickly, without sending them through another confusing process.
All three have a point. The trouble starts when their targets pull them in different directions.
An extra identity check may protect an account, but it can also leave a customer struggling to get help. Removing that check may make service quicker while making it easier for someone to pretend to be the customer. The person answering the phone gets caught between the rules and the person who needs assistance.
But making people struggle should never be treated as proof that security is working. Some changes improve both safety and ease. Passkeys, for example, can let people sign in using the familiar way they unlock their device, while making fake login pages less effective at stealing access.
Clear explanations matter too. HTTP does not encrypt a connection. HTTPS does, but it protects the connection between your browser and a website. It cannot promise that the company keeps all your information safe, and a fraudulent website can use HTTPS too.
People need to understand what a protection does and where its limits are. And the teams designing that protection need to understand how people actually use it.
When a risk gets a price tag
Money is often the language that gets attention. Lost sales, recovery costs, possible fines and damage to a company’s reputation make a warning easier to understand.
That is a useful translation. Preventing disruption helps a business survive. But it worries me when the financial argument becomes the only argument. A customer’s privacy should matter even when protecting it brings no obvious profit.
Prevention also has an awkward problem: when it works, nothing dramatic happens. There is no headline about the working day that went ahead normally. It can be easier to see the cost of protection than the damage it prevented.
Recent incidents show what disruption and exposure look like. In October, the incident at Ahold Delhaize disrupted Albert Heijn’s online services. Its 19 October update said there was no evidence at that point that sensitive customer, employee or partner data had been taken.
Odido’s February attack affected approximately 6.39 million people, according to the company. The exposed information differed between people and included contact, banking and identification details.
These cases show the consequences. They do not tell us, by themselves, which warnings were given beforehand or how leaders responded.
Attackers also have different aims. Dutch cybersecurity assessments describe threats from state actors, criminals and others. Some seek money; others pursue intelligence or disruption. Whatever their goal, ordinary people can end up paying the price.
“The company has insurance” is a poor excuse for causing harm. Insurance cannot make stolen information private again. It cannot return someone’s lost time or automatically restore their trust.
Making one world understandable to another
Much of my life has involved trying to make something understandable to someone else.
Sometimes that meant YouTube or Twitch videos. Sometimes it meant graphics or stories. At work, it meant helping people understand matters involving HR, finance, IT incidents or services without expecting them to become experts first.
The task was similar each time: work out what the other person needed to understand, and find words or examples that meant something to them.
In Dutch, we call this “Jip en Janneke language”. For me, that means explaining something clearly enough that someone can use the information.
“Service availability” can sound distant. “You may be unable to order groceries” tells someone what the problem could mean for their day. Both describe the same issue, but one is much easier to connect with.
I also tend to notice links between problems being discussed separately. That can help identify a risk early. It still needs checking. Seeing a pattern should lead to questions and evidence, with room to discover that the first explanation was wrong.
Wanting to contribute beyond my own work also brought me into a political party’s defence and security activities. My interest was cybersecurity and awareness: helping people understand how digital risks affect society.
Public involvement also left me feeling more exposed and scrutinised. That can make speaking openly harder.
Confidentiality adds another difficulty. People working with sensitive information cannot always share everything they know. They still need trusted ways to raise concerns with someone able to investigate and act.
That is where explanation meets responsibility. A warning needs somewhere to go.
If raising a concern makes someone look difficult, expensive or disloyal, people may become quieter. The problem can remain. Protecting a reputation should include taking uncomfortable information seriously.
New technology, the same divide
I see similar gaps in the way we talk about AI.
Someone in a company may see a tool that saves hours. A freelance illustrator may wonder whether it threatens their income. A writer may enjoy using it to explore ideas while worrying about what happens to ownership and credit.
As a creator, I can see value in AI as an “inspirational assistant”. It can help me explore possibilities, ask questions and test a different approach.
That does not settle another creator’s concerns about consent, payment or the value of their work. Those deserve a proper conversation. Calling someone afraid of change will do little to help them trust the people introducing it.
The same courtesy should extend to people who choose to experiment. Using a tool does not explain every choice someone makes with it.
A better discussion starts with the particular use. What does it help with? What could it harm? Who benefits, and who carries the risk? What support would people need to make an informed choice?
Data centres raise similar questions. They help keep digital services running, but they also use physical space and resources. The International Energy Agency describes pressures involving electricity networks, emissions and water, alongside the importance of digital infrastructure.
One person sees capacity for the future. Another sees a development near their home and wonders what it means for local resources and costs.
Understanding why data centres matter should help us discuss those concerns properly. It should also help us distinguish between different proposals. What will this one support? How will its resource use be managed? What will the community gain, and what will it have to live with?
People can understand a proposal and still disagree with it. Clear explanation should help them judge the choices, including the costs of accepting or rejecting them.
Listening needs a next step
We need people who can translate between these worlds. We also need people willing to listen to the translation.
That means asking what someone is trying to protect. Their customers? Their job? Their creative work? Their local environment? Their ability to keep a business alive?
Understanding that gives a conversation somewhere useful to begin.
But communication alone cannot solve every disagreement. Sometimes people understand a risk and still benefit from leaving it with somebody else. That is why listening has to connect to responsibility.
Who will look into the concern? Who can make a decision? What information is missing? When will there be an answer?
Those are simple questions, but they turn “we hear you” into something people can check.
The person raising a problem should not have to spend months translating it, defending it and chasing it before anyone else takes ownership.
And those of us giving warnings have work to do too. We need to explain uncertainty, hear other concerns and remain willing to change our minds. Otherwise, we risk building another island.
We cannot leave these choices to some future artificial general intelligence, or keep treating the planet’s limits as tomorrow’s problem. We have decisions to make now, with the knowledge and tools already available.
I do not want to collect more moments of “I told you so”.
I want more moments when someone says: “I understand what you mean. Let’s work out what we can do.”
And then we do it.